Glossary · Security & Resilience
What is zero trust security?
Short answer
Zero trust is a security model built on the principle “never trust, always verify”: no user, device or service is trusted just because it is inside the company network. Every request is authenticated, authorised and checked against current context, and each identity gets only the minimum access it needs, which limits how far an attacker can move after a breach.
Core principles
- Verify explicitly: authenticate and authorise every request using identity, device health and context, not network location.
- Least privilege: grant just enough access, for just long enough.
- Assume breach: segment systems, encrypt traffic internally and monitor continuously, so a compromise stays small.
What it looks like in practice
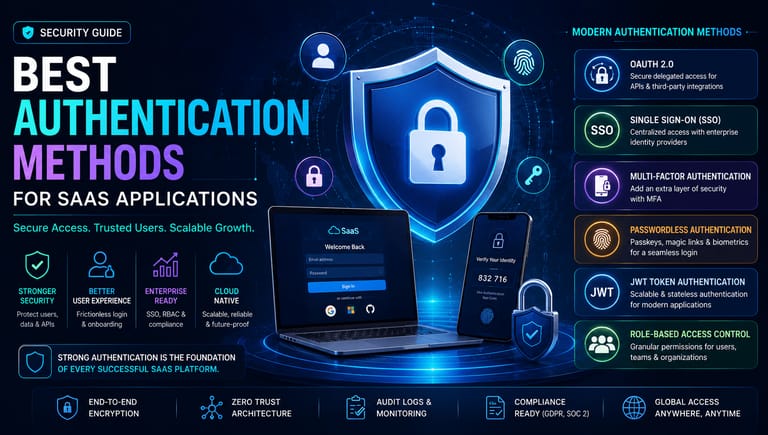
- Single sign-on with multi-factor authentication for every employee app, replacing VPN-only access.
- Service-to-service authentication with short-lived tokens or mutual TLS.
- Fine-grained permissions in applications, reviewed regularly.
- Central logging and alerts on unusual access.
For application teams
Zero trust also applies inside your code: validate every input, check authorisation on every endpoint (not just the UI), use short-lived credentials such as JWTs with tight expiry, and treat AI components as untrusted actors that need the same checks.